Log4Shell: Critical Log4j RCE Vulnerabilty -- Update to Version 2.15.0
On Dec.10, 2021, a new, critical Log4j vulnerability was disclosed: Log4Shell. All current versions of log4j2 up to 2.14.1 are vulnerable.
On Dec.10, 2021, a new, critical Log4j vulnerability was disclosed: Log4Shell. All current versions of log4j2 up to 2.14.1 are vulnerable.
The Java 17 LTS release brings you significant improvements to prevent malicious deserialization in your java applications.
Our research team found a correlation between socially trending vulnerabilities and the existence of exploits that can harm your …
A discussion with some great folks in the Java world about the highlights of the Snyk Java Ecosystem report and current developments in …
If you are still running on an old Maven version like 3.6.3 or below, you need to upgrade to version 3.8.1 because of security reasons.
Learn how to begin with Snyk for secure Java development so that you too can be more secure from the get-go!
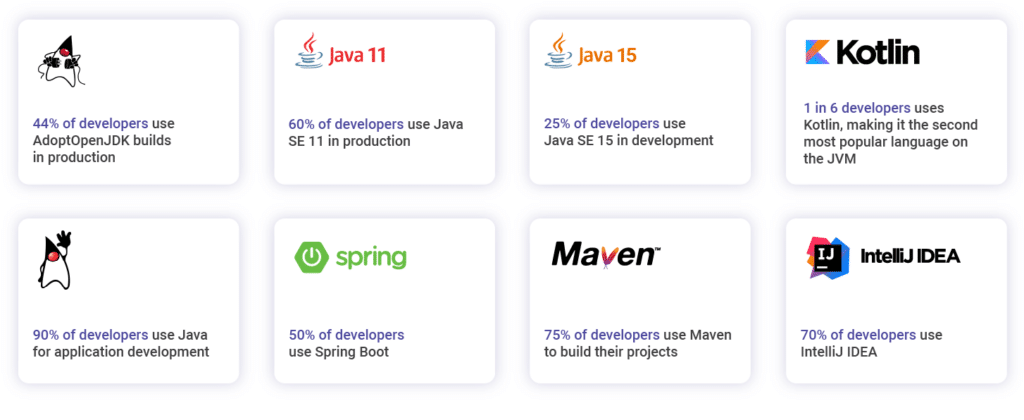
JVM Ecosystem Report 2021 presents the results of the largest annual survey on the state of the JVM ecosystem.
What is a strong encryption algorithm today, might be a weak algorithm a year from now. Therefore, encryption needs to be reviewed …
Cross-site scripting (XSS) is a well-known issue and mostly utilized in JavaScript applications. However, Java is not immune to this!
With anchors, you can create a YAML bomb! The tremendous amount of (nested) objects will cause a memory overload.