Namespace Shadowing (a.k.a. “Dependency Confusion”) Attack
The npm Registry is vulnerable to supply chain namespace shadowing, also known as “Dependency Confusion” attacks!
The npm Registry is vulnerable to supply chain namespace shadowing, also known as “Dependency Confusion” attacks!
Automate Java applications continuous integration and delivery with pre-configured master-slave Jenkins cluster from Jelastic PaaS.
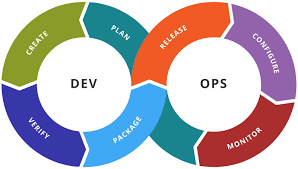
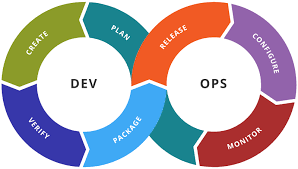
DevOps has a ton of jargon in it, though. It’s like running into a brick wall. Here, I'll explain package managers!
I’m covering tools and terminology common to DevOps, plus the occasional newbie-friendly tutorial for emerging or established technologies.
I’ll cover tools and terminology common to DevOps, plus the occasional newbie-friendly tutorial for emerging or established technologies.
Learn about the internals of image layering created by container image builder Jib and explore what distroless images are and their …
What are the quick wins or low hanging fruits if you want to deal more with the topic of security in software development?
DataStax Astra Service Broker: seamlessly integrate Cassandra into your Kubernetes deployments and leave the operations to somebody else!