New Java 17 Features for Improved Security and Serialization
The Java 17 LTS release brings you significant improvements to prevent malicious deserialization in your java applications.
The Java 17 LTS release brings you significant improvements to prevent malicious deserialization in your java applications.
In this article, I will limit the coverage of Java 17 to its language features – Sealed Classes and Pattern Matching for switch.
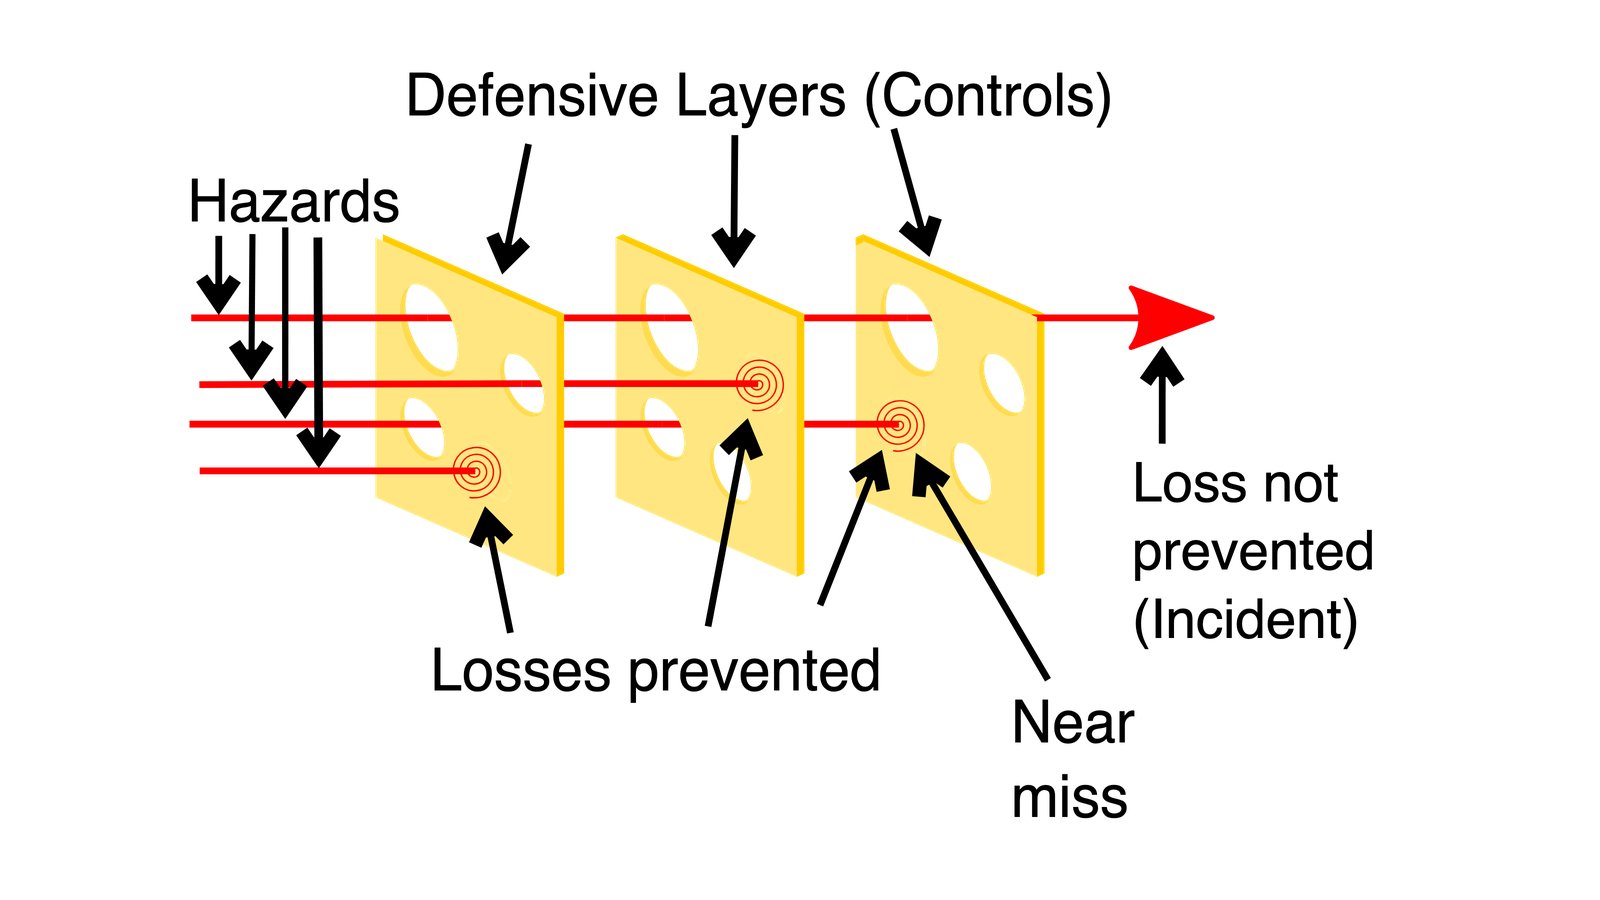
Java, like most platforms or languages has layers of security, this article lookS at the Authorization layer and how JEP 411 relates to it.
SecurityManager, foundation to build secure software, on its own is insufficient to limit users & software to the least privilege principle.
Unified logging was introduced in JDK 9, let's begin with a recapitulation of JEP-158, laying out the foundation of JVM unified logging.
In this article, I will try to explain the new feature, from Java 10, local variable type inference using the reserved type name "var".
Hidden classes allow frameworks to define classes as non-discoverable implementation details, so that they cannot be linked against. Read …
If OpenJDK is the background source for your livelihood, you might want to contribute to future development of the OpenJDK. Find out how!
Unlike sealed classes, hidden classes (JEP 371) are a JVM rather than a language-level feature, aiming not to change the Java language.