Java Security: Log4J, the SecurityManager, and Funding
A demonstration of log4j exploits, which defenses people tried, and which worked. We'll cover how groups responded effectively to patch to …
A demonstration of log4j exploits, which defenses people tried, and which worked. We'll cover how groups responded effectively to patch to …
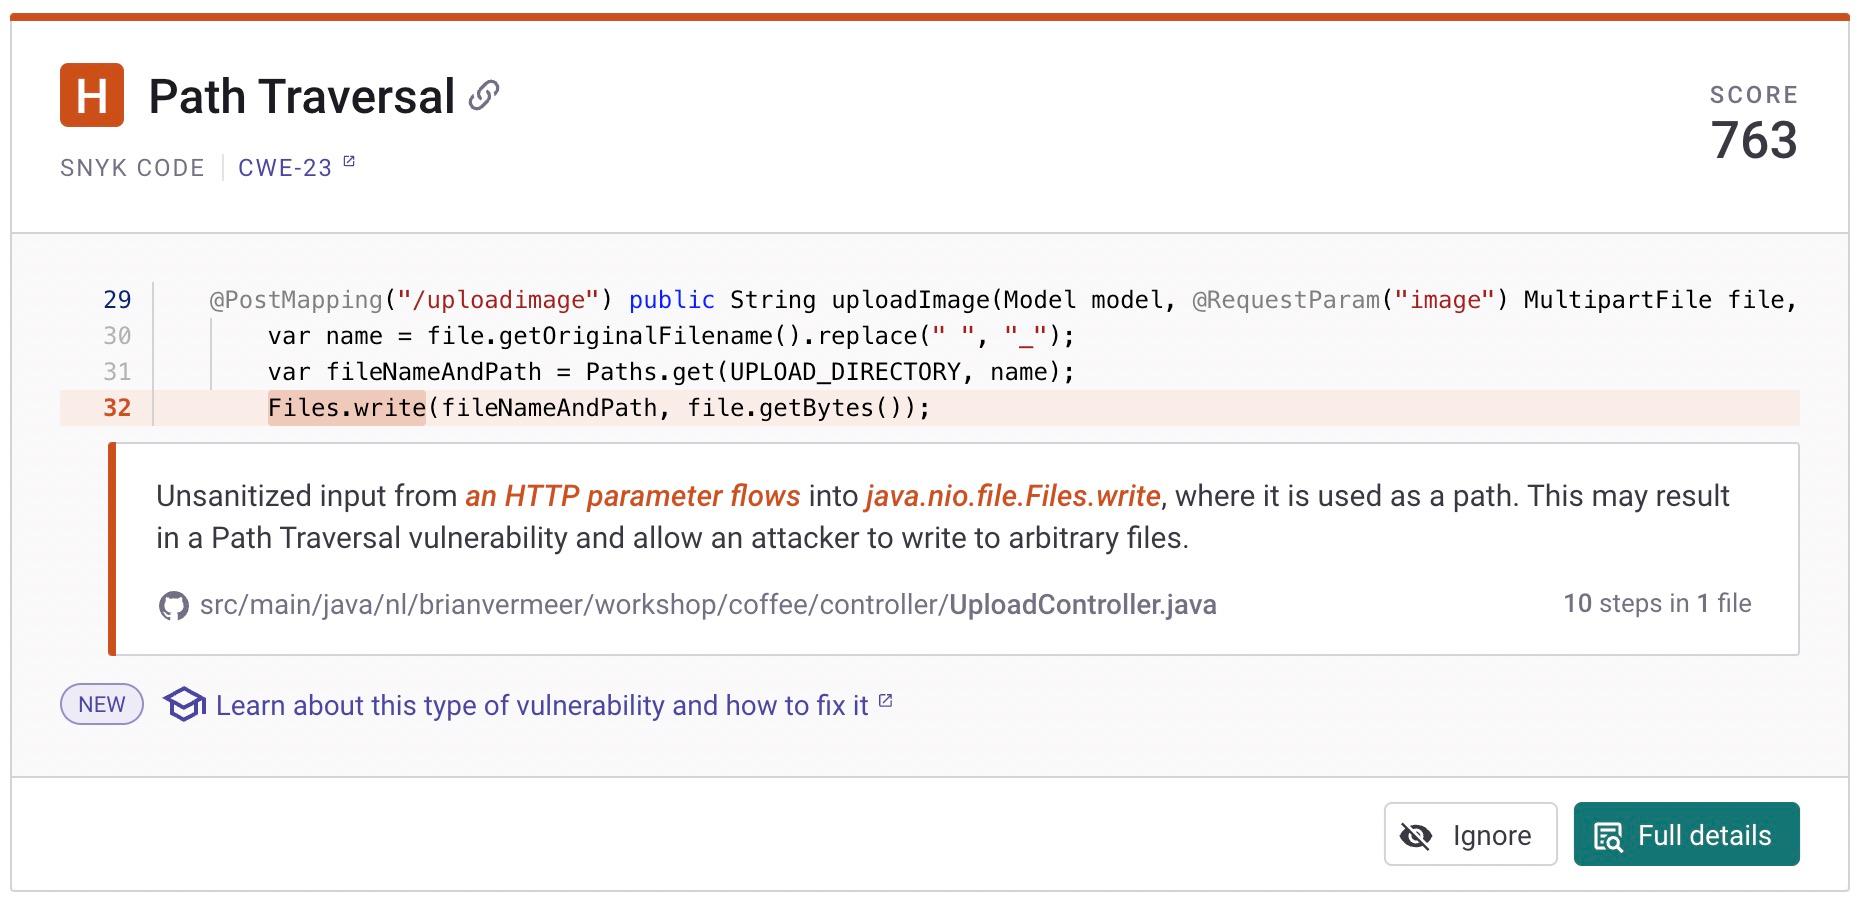
Path traversal vulnerabilities are a serious threat to Java web applications, amongst the top security issues Snyk finds in Java code.
Next time you’re considering a new Java library, look for the Sonatype Safety Rating on Maven Central to aid in your decision making.
Java is a compiled language, so you should create an SBOM whenever you build a release version of your application. Find out more here!
Externalizing your authentication process to a third party may be sensible, but avoid binding your infrastructure to its proprietary …
The third article in a series on SBOMs, software supply chains, the government and you, introducing threat modelling and tools to help!
Simple configuration that requires no code change can save you from hacks such as Log4Shell, & from vulnerabilities we don't know about yet!
Learn how you can leverage OPA and Apache APISIX to move your authentication and authorization logic from the code to the infrastructure.
Let's learn all about software composition analysis, how they work and why it is important for developers to get started as soon as …
Keeping your Java environment stable requires discerning which updates to install and then installing them appropriately.