Hacking Java XML Input via External Entity Injection
In this video, I explain and demonstrate how an XXE injection attack works by extracting system data that should not be exposed.
In this video, I explain and demonstrate how an XXE injection attack works by extracting system data that should not be exposed.
Given I love a good puzzle (especially the Java Puzzles), let’s try some puzzles, using the Java syntax only, without any runtime behavior.
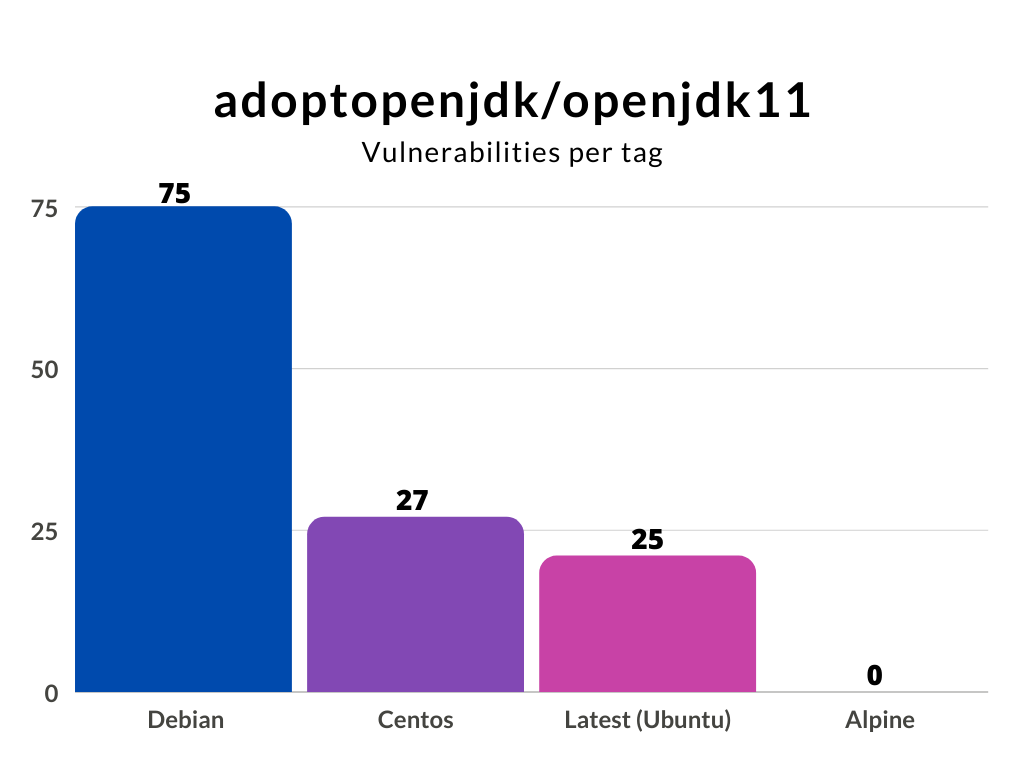
Naively creating custom Docker images for Java apps comes with security concerns. How do we make security an essential part of Docker …
United by their passion for open source, Payara and IBM recently teamed up for a panel discussion on security in Java application …
Tip: By distinguishing between the SQL code and the parameter data, the query can’t be hijacked by malicious input.
If you need to Deserialize an inputstream yourself, you should use an ObjectsInputStream with restrictions.
With XML eXternal Entity (XXE) enabled, it is possible to create a malicious XML, and read the content of an arbitrary file on the machine.
This presentation by Ondrej Mihalyi at DevOpsCon showcases the strength of combining MicroProfile and an OAuth service.
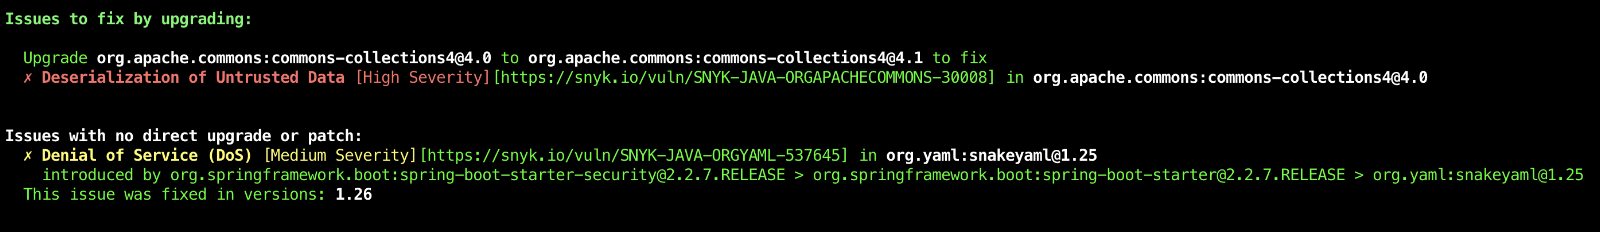
In this article, I will explain how you can fix vulnerabilities in third-party libraries when using Maven, even when it is not obvious.
For Java developers who depend on OpenJDK, foojay is the place to be for comprehensive dashboards, insights, analysis, and blogs. Read More!