 Steve Poole
2,406 views
Spring Boot 3.5 Migration and the CRA: When Good Enough Isn't"
Spring Boot 3.5 reaches EOL on June 30. The legal context is about to change. Here's what 'without undue delay' means when commercial …
Steve Poole
2,406 viewsSpring Boot 3.5 reaches EOL on June 30. The legal context is about to change. Here's what 'without undue delay' means when commercial …
 Iryna Dohndorf
2,710 views
Tiberius: A Security Testing Framework for LLM Applications in Java How do you write a regression test for a system that is …
 Cristobal Escobar
1,367 views
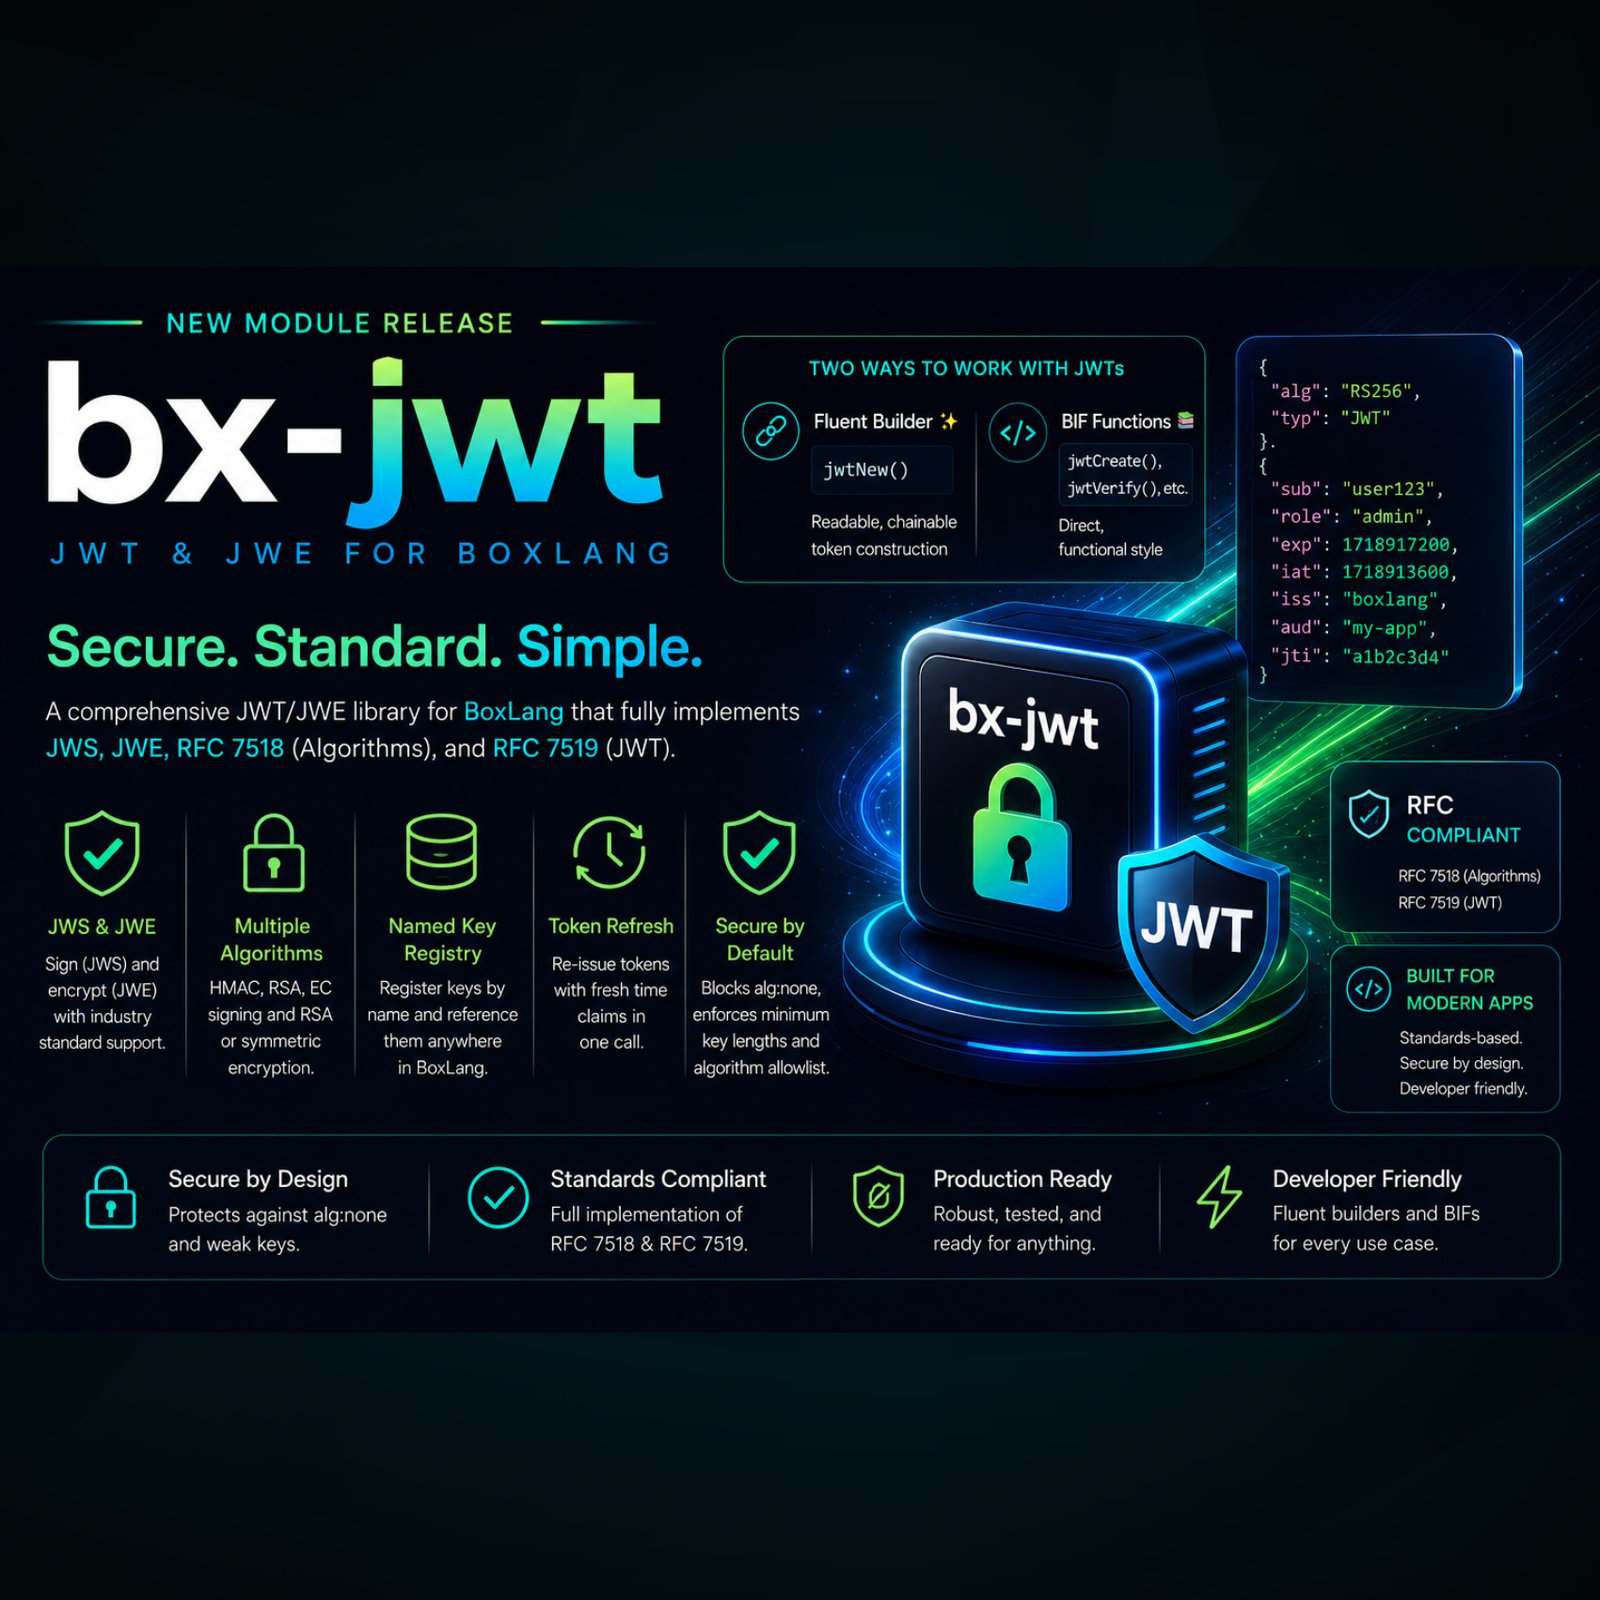
JWT authentication is everywhere. But rolling it correctly — with proper algorithm enforcement, key management, clock skew handling, JWE …
Cristobal Escobar
1,409 viewsBoxLang 1.13.0 is a stability-first release with deep compatibility work and runtime hardening. This build closes 48 issues, with the …
 Brian Vermeer
1,078 views
The Thymeleaf vulnerability with a CVSS score of 9.1 grabs your attention, as it should. But before you call the cavalry and claim this as …
 966 views
Is your Java application actually secure, or does it just look that way? In this episode of the Foojay Podcast, Frank is joined by Steve …
Steve Poole
3,804 viewsSpring Boot 3.5 goes EOL June 30, 2026. But the real risk isn't the migration. It's what happens to CVE reporting once a project reaches end …
Steve Poole
2,225 viewsAI coding tools sound confident even when they're wrong. Here's the psychology behind why Java developers accept bad suggestions — and …
 Jonathan Vila
11,464 views
Master AI agents with 5 developer best practices for building scalable architecture with MCP, subagents, context isolation, and guardrails.
 Hüseyin Akdoğan
5,069 views
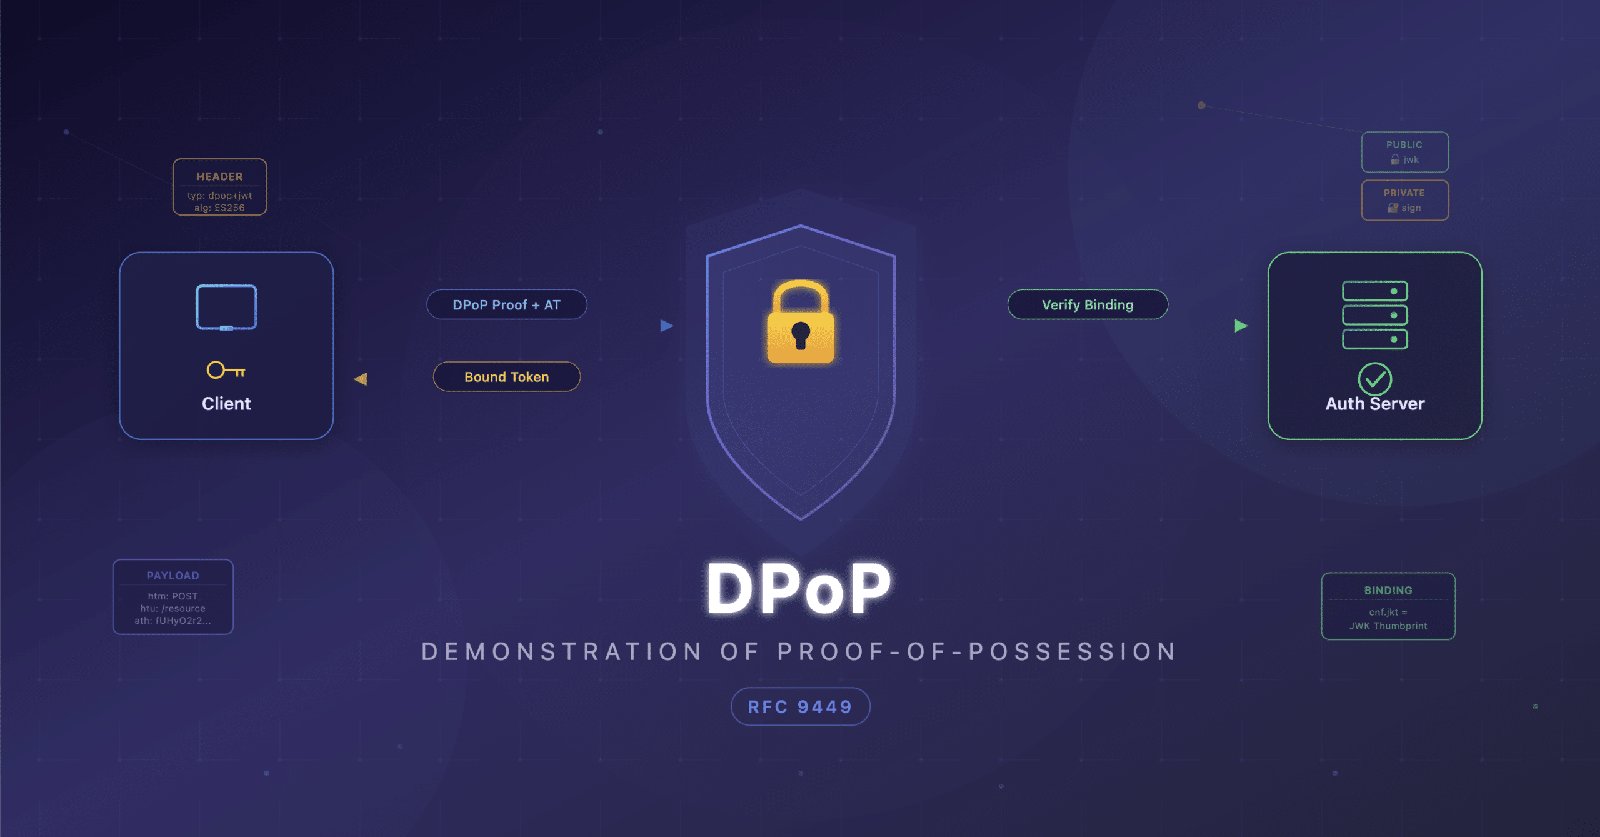
DPoP is one of the most exciting developments in the IAM (Identity and Access Management) space in recent years. Yet many backend developers …