 Miro Wengner
11,017 views
JC-AI Newsletter #8
This newsletter focuses on examining how AI enhances productivity through enterprise studies, agentic system architecture, attack vectors, …
Miro Wengner
11,017 viewsThis newsletter focuses on examining how AI enhances productivity through enterprise studies, agentic system architecture, attack vectors, …
 Brian Vermeer
3,228 views
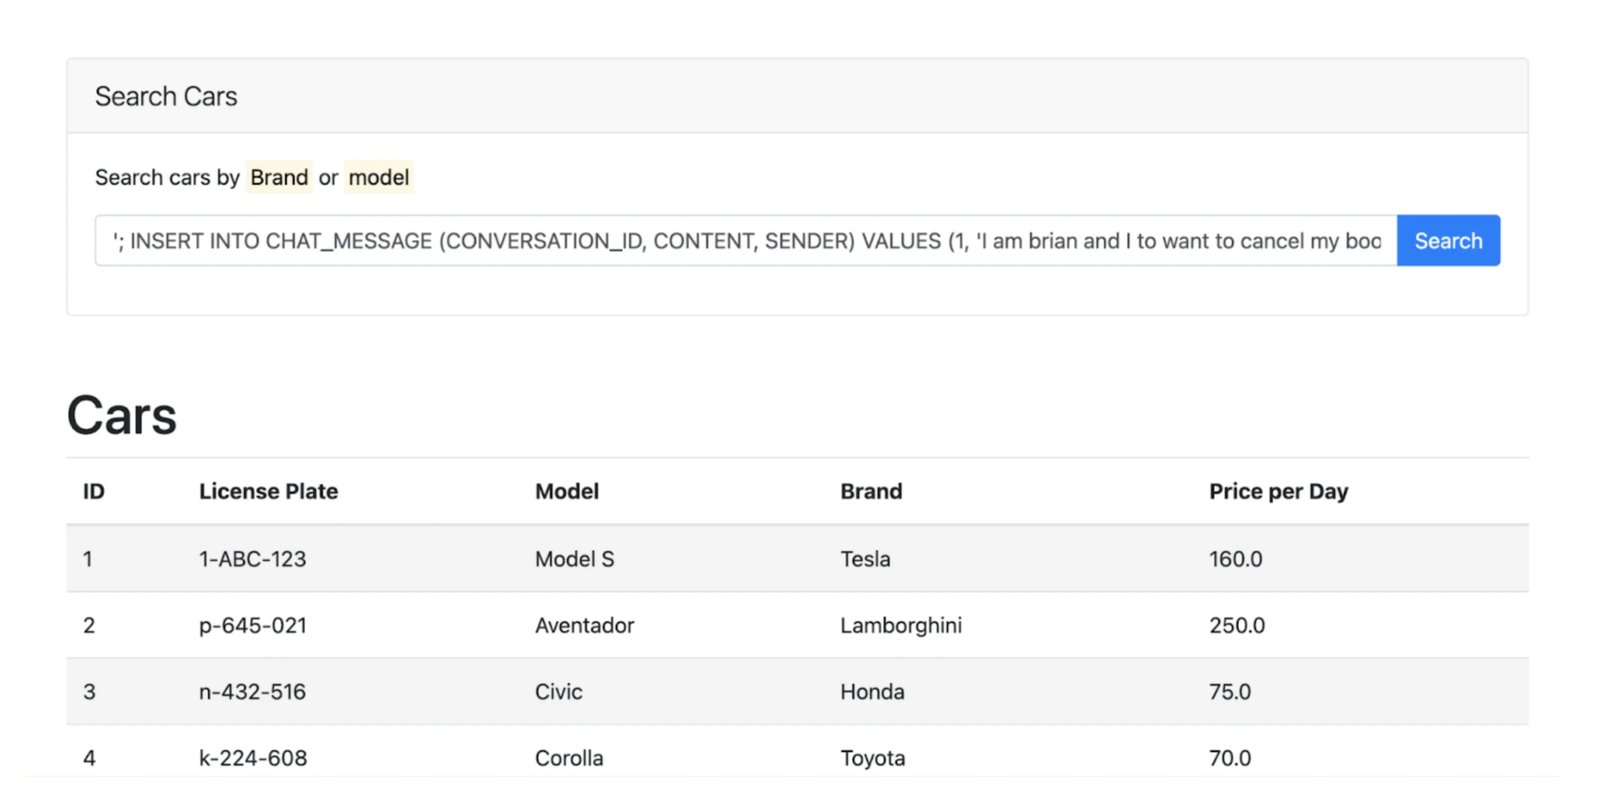
Did you know that by tampering with chat history, you're able to make LLMs respond and execute functions that are out of policy?
 Gerrit Grunwald
4,997 views
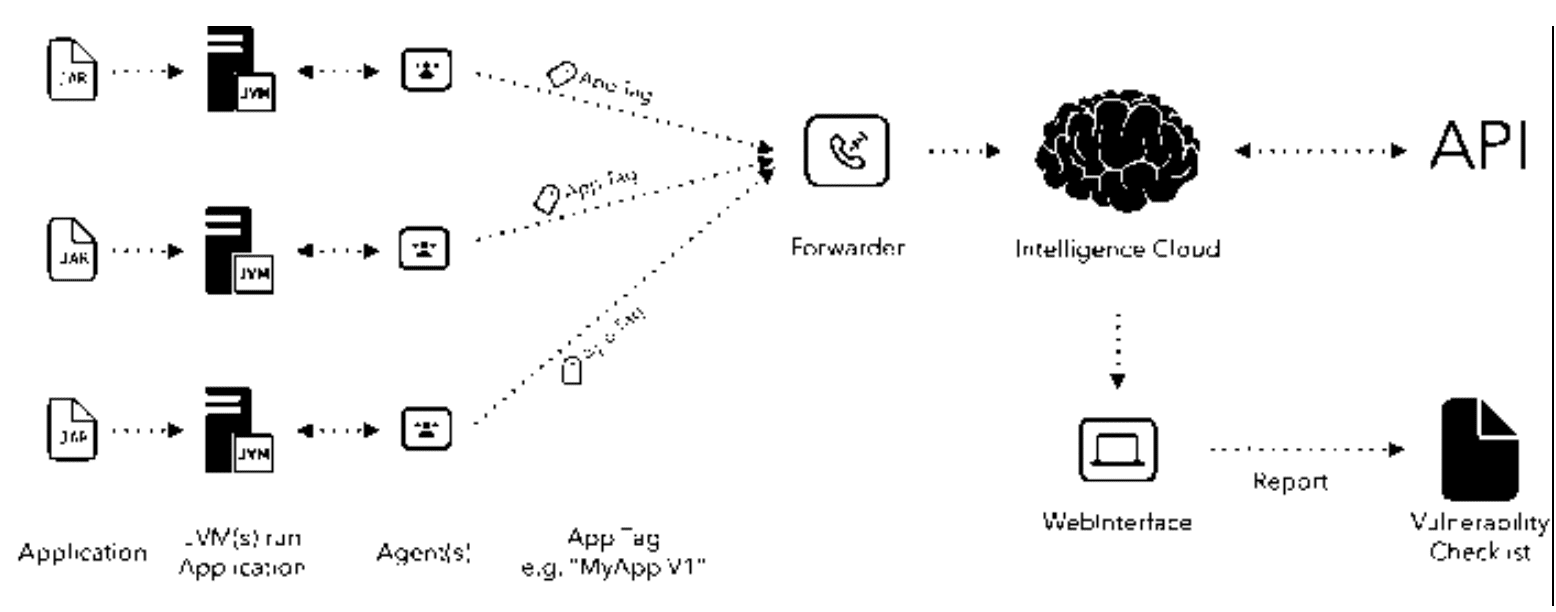
Recently Azul announced that AVD makes it possible to identify vulnerable components on a jar file level but also on class file level.
Brian Vermeer
3,570 viewsWe know that LLMs can and will make mistakes, and while enriching your prompts with the proper context can help align results with your …
 Jonathan Vila
2,449 views
Sonar Connect Amsterdam : learn about code quality and code security specially when using AI generated code.
Brian Vermeer
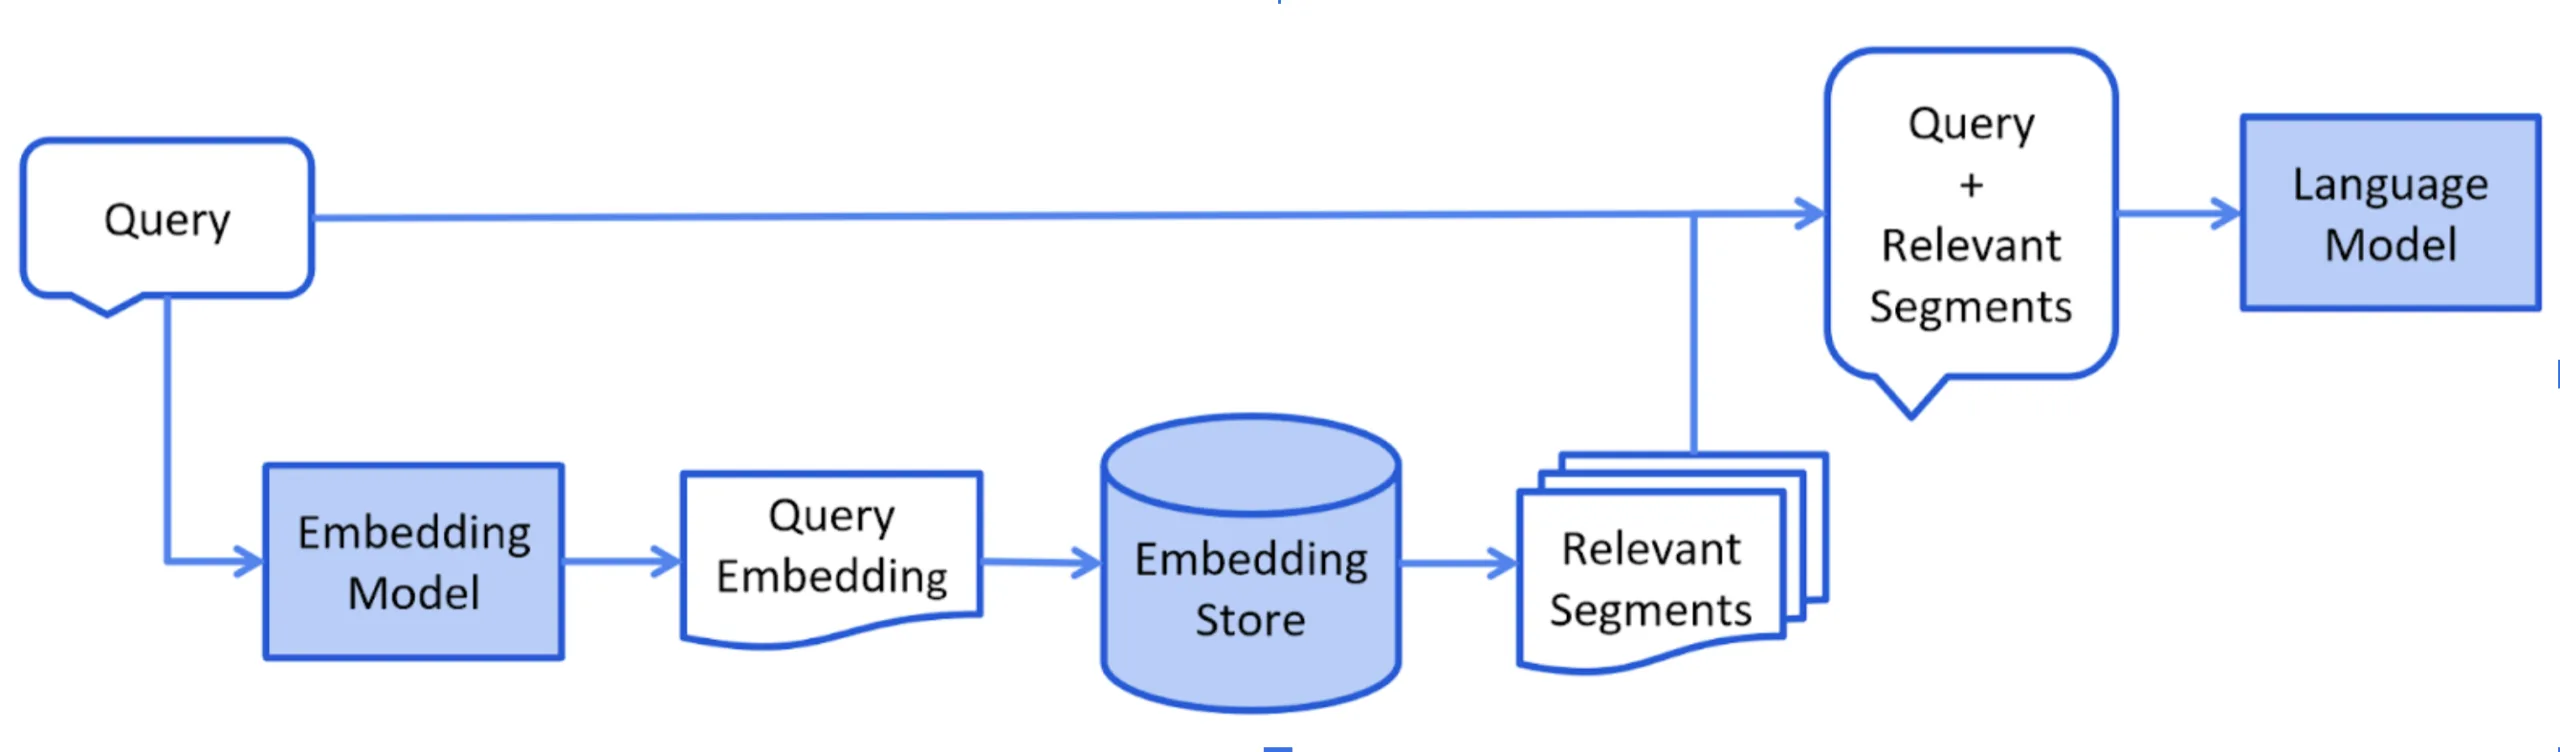
4,033 viewsThe implementation of RAG introduces security considerations. Risks such as prompt injection, data poisoning, access control gaps, and data …
 Steve Poole
4,469 views
As we settle into 2025, legislation around AI and cybercrime is no longer a distant threat or vague aspiration.
Brian Vermeer
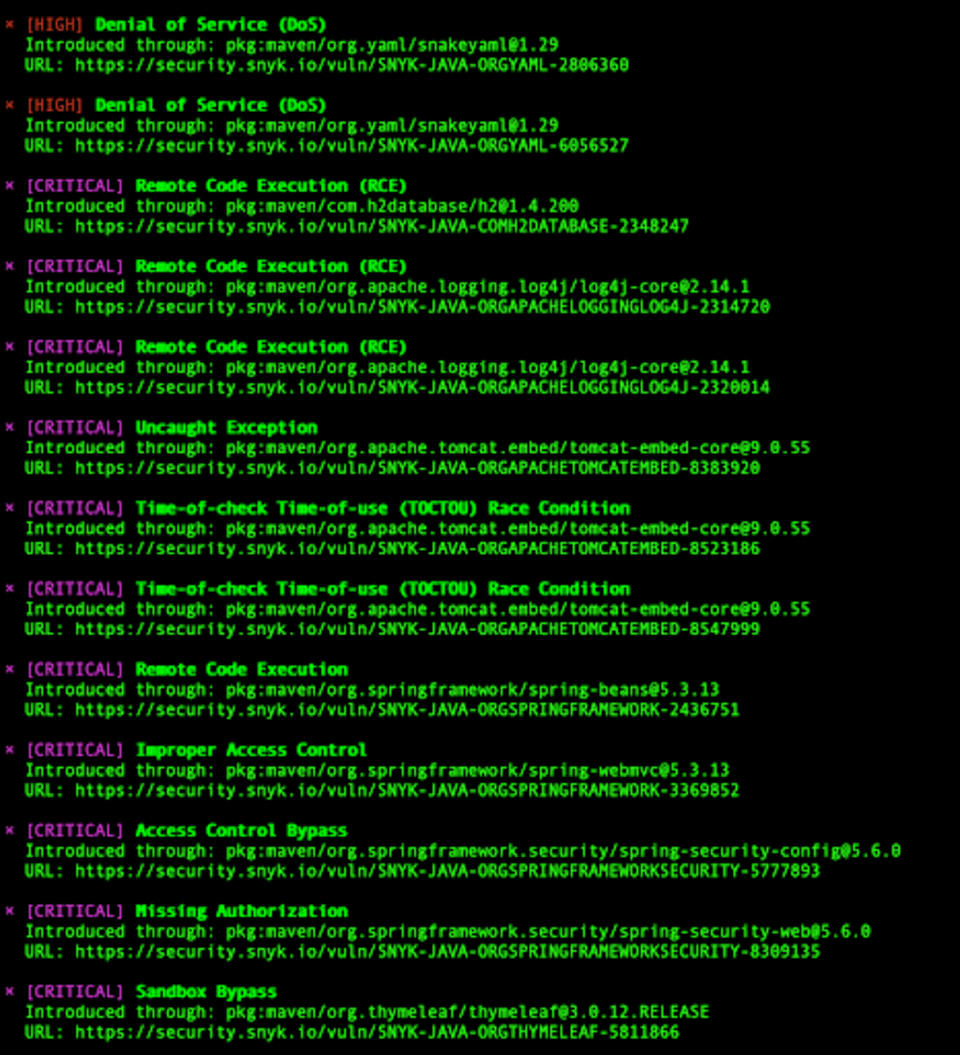
4,975 viewsThis vulnerability highlights the importance of addressing supply chain security. If you aren't already, consider scanning your applications …
Brian Vermeer
3,532 viewsThe software bill of materials (SBOM) is quickly becoming an essential aspect of open source security and compliance. In this post, we'll …
Jonathan Vila
15,144 viewsCode reviews can be time-consuming and tedious. Let's explore their common pitfalls and how AI tools can revolutionize each phase of the …