 Brian Vermeer
6,814 views
How to create SBOMs in Java with Maven and Gradle
Java is a compiled language, so you should create an SBOM whenever you build a release version of your application. Find out more here!
Brian Vermeer
6,814 viewsJava is a compiled language, so you should create an SBOM whenever you build a release version of your application. Find out more here!
 Nicolas Frankel
7,723 views
Externalizing your authentication process to a third party may be sensible, but avoid binding your infrastructure to its proprietary …
 Dan Conn
5,987 views
The third article in a series on SBOMs, software supply chains, the government and you, introducing threat modelling and tools to help!
 Shai Almog
10,251 views
Simple configuration that requires no code change can save you from hacks such as Log4Shell, & from vulnerabilities we don't know about yet!
Nicolas Frankel
2,546 viewsLearn how you can leverage OPA and Apache APISIX to move your authentication and authorization logic from the code to the infrastructure.
 Jamie Coleman
6,517 views
Let's learn all about software composition analysis, how they work and why it is important for developers to get started as soon as …
 Frank Delporte
8,229 views
Keeping your Java environment stable requires discerning which updates to install and then installing them appropriately.
 Erik Costlow
5,525 views
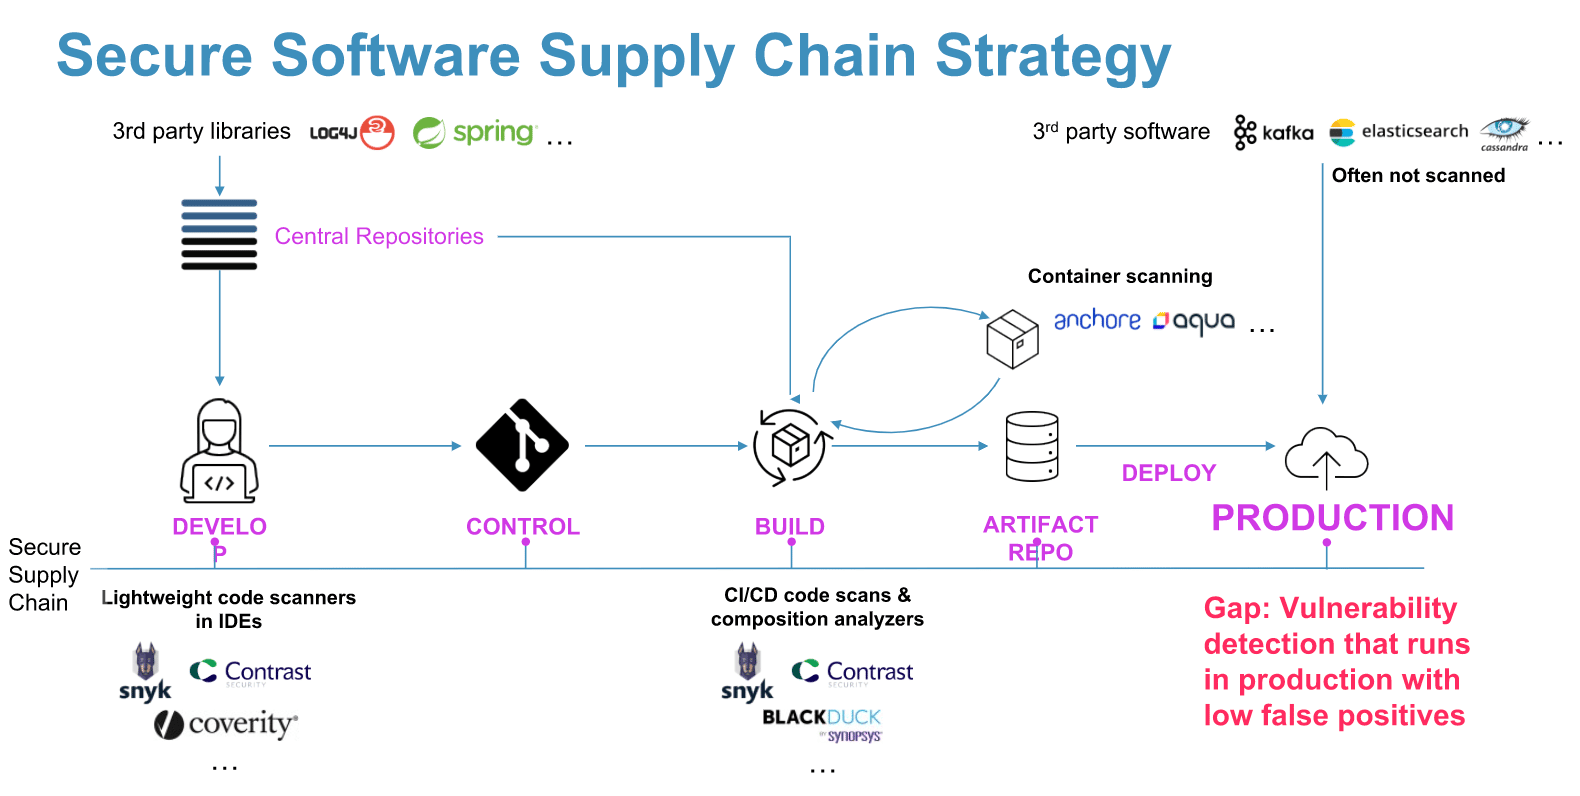
With Azul Vulnerability Detection, running the software and getting security insight become the same action.
 Steve Poole
5,921 views
Software bill of materials, anyone? A year ago, developers had not heard of the 'SBOM' acronym... and now SBOM visualiser called BOM Doctor.
 Marit van Dijk
5,234 views
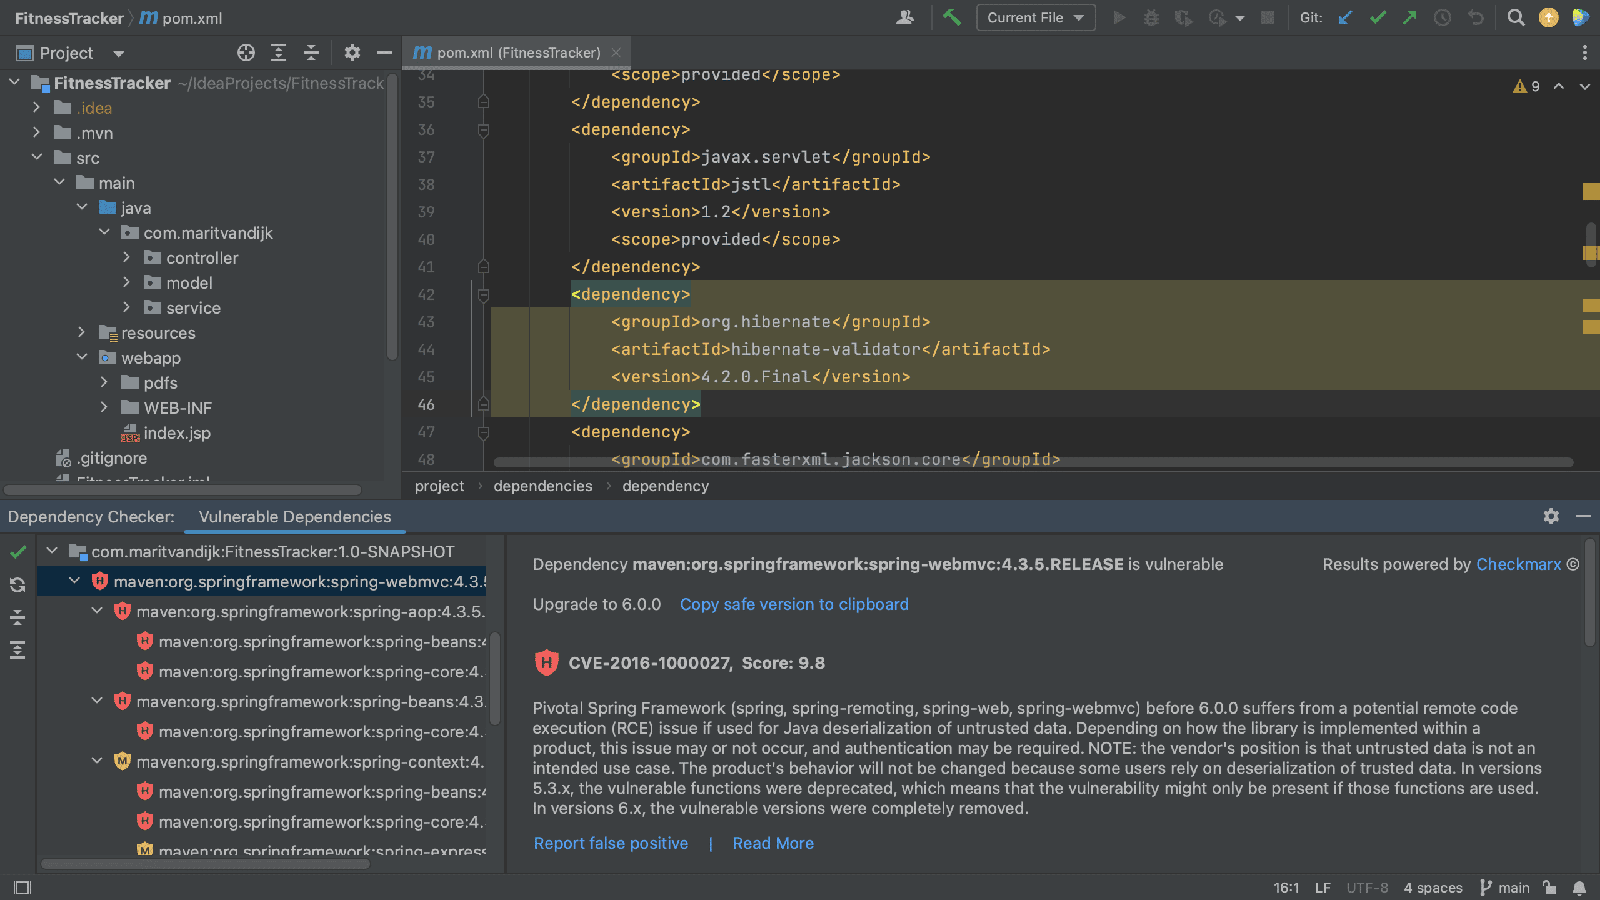
In this article, we're going to take a look at the Package Checker plugin, that's bundled with IntelliJ IDEA Ultimate!