Use Query Parameterization to Prevent Injection
Tip: By distinguishing between the SQL code and the parameter data, the query can’t be hijacked by malicious input.
Tip: By distinguishing between the SQL code and the parameter data, the query can’t be hijacked by malicious input.
Being lazy isn't a bad thing, it's an efficiency gain for focusing on the things that matter, which isn't checking my parentheses are …
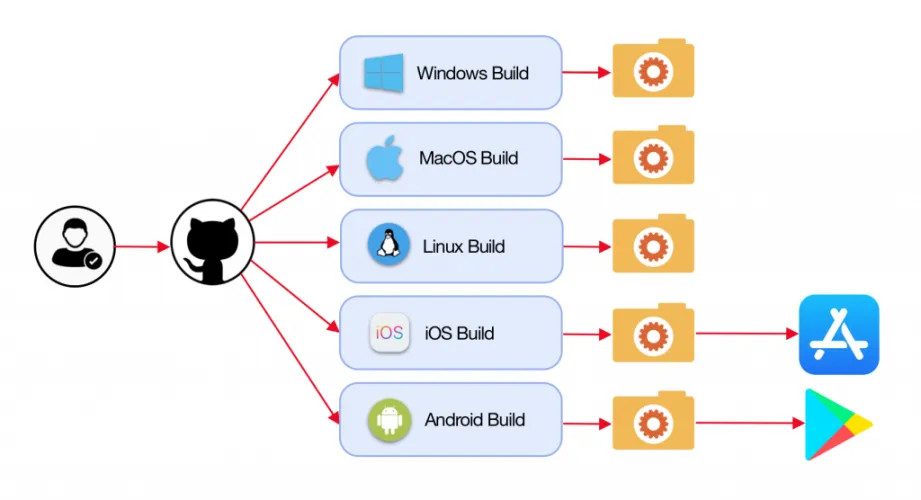
How to build native applications for multiple devices from a single JavaFX project with Gluon Mobile and GitHub Actions.
Azul has made Zulu OpenJDK builds of OpenJDK 8, 11, and 13, as well as 16-ea, available on Apple Silicon, Arm-based Macs. Check it out!
With the Software ECG Covid-19 Edition, you can evaluate the most important Covid-19 time series across countries. Read on for details!