Small, Signed, and Still Vulnerable? What Really Makes a Java Container Secure
Small, distroless, signed, and scanned clean, yet vulnerable? Six Java container security myths taken apart and gaps closed.
Small, distroless, signed, and scanned clean, yet vulnerable? Six Java container security myths taken apart and gaps closed.
Fail fast, pin every version, let profiles switch themselves and get an SBOM for free: practical Maven techniques from POMs in daily use.
A lightweight, pip-inspired dependency manager and runner that makes exploring GitHub Java projects simple, without the usual Maven or …
My current company has settled on using Gradle. It doesn't make me very happy, but you need to learn to work with constraints. Plus, I must …
I've been a big fan of Renovate for a couple of years already. Renovate scans your repositories, detects outdated package versions, and …
Every production application carries secrets: database passwords, API tokens, encryption keys. The question is never whether to manage them …
BoxLang 1.15.0 is a high-impact release with two big headlines and a long tail of hardening. The first headline is a massive performance …
If you build Java on GitHub Actions, actions/setup-java is almost certainly the first step in your workflow. It installs a JDK, wires up …
I recently had the pleasure of joining the Foojay podcast to talk about Quarkus in depth. The conversation covered a lot of ground, from …
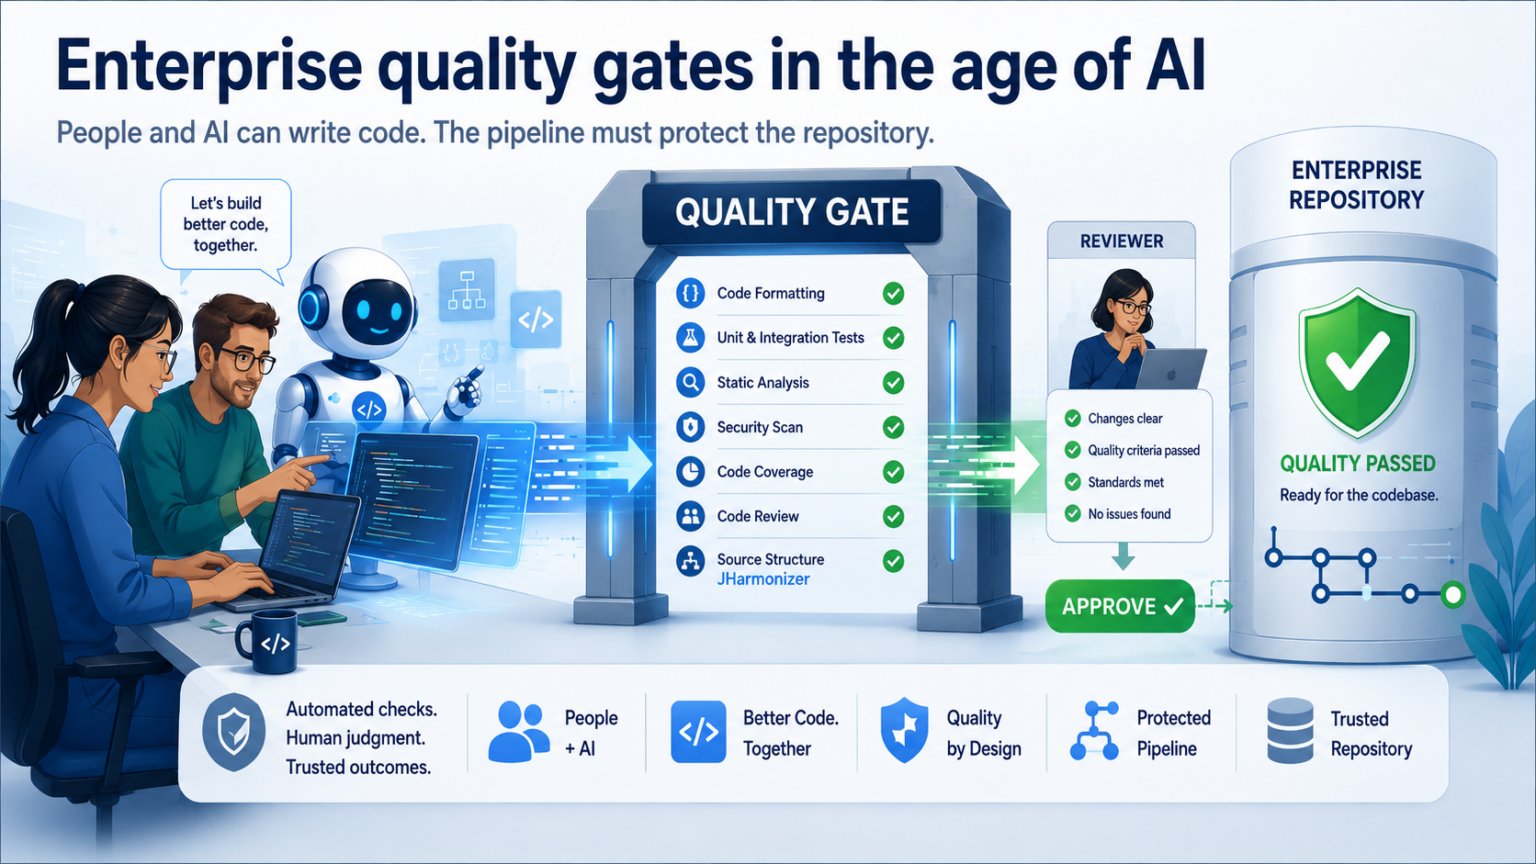
Learn how enterprise Java teams can use deterministic quality gates, CI checks and tooling to keep AI-assisted code reviewable, consistent …